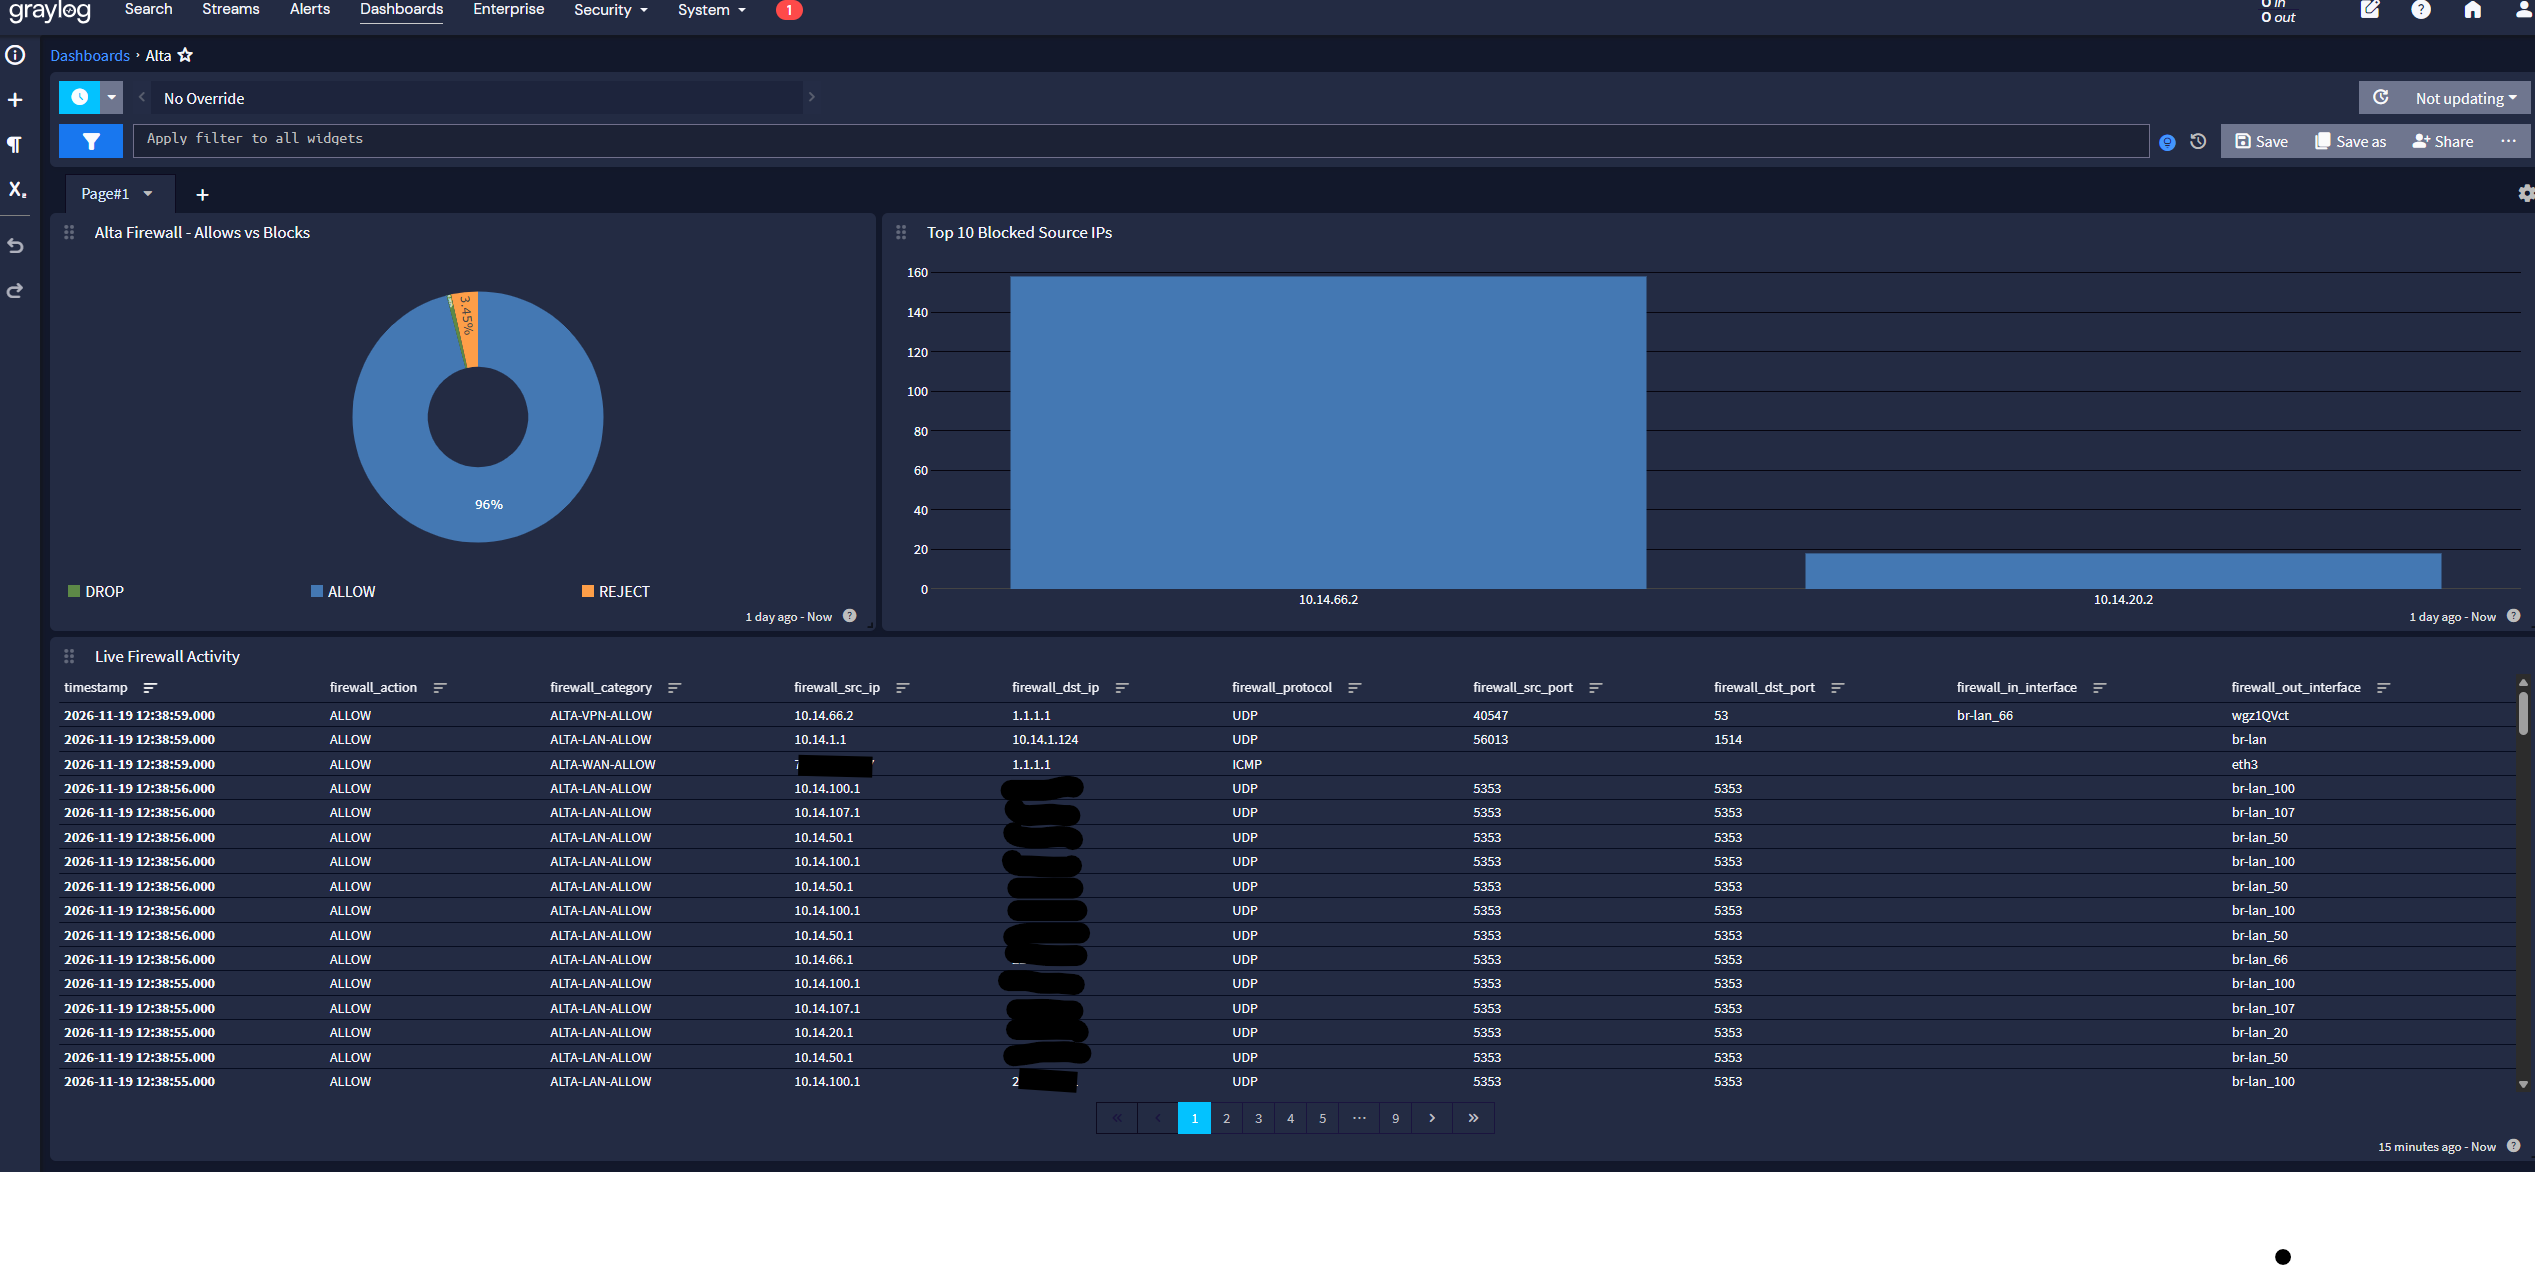
If you are like me I like very detailed logs. I created a script that you can add to your post.cfg. Logs your allowed traffic and dropped traffic to see everything working

# ============================================
# 2. Firewall Logging to Graylog
# ============================================

# Log only NEW connections and rate-limit events.
# LOG is non-terminating; existing firewall
# decisions remain in place.

LOG_LIMIT="10/min"
LOG_BURST="20"

# Create dedicated logging chains.
iptables -N ALTA_LOG_ALLOW 2>/dev/null
iptables -N ALTA_LOG_DROP 2>/dev/null

# Flush only our custom logging chains.
iptables -F ALTA_LOG_ALLOW
iptables -F ALTA_LOG_DROP

iptables -A ALTA_LOG_ALLOW \
    -m conntrack --ctstate NEW \
    -m limit --limit "$LOG_LIMIT" \
    --limit-burst "$LOG_BURST" \
    -j LOG --log-prefix "ALTA-FW-ALLOW: " \
    --log-level 6

iptables -A ALTA_LOG_DROP \
    -m limit --limit "$LOG_LIMIT" \
    --limit-burst "$LOG_BURST" \
    -j LOG --log-prefix "ALTA-FW-DROP: " \
    --log-level 6


# ============================================
# 3. Log LAN/VLAN Allow Decisions
# ============================================

# Insert immediately before terminal ACCEPT
# decisions in the shared LAN destination chain.

iptables -C zone_lan_dest_ACCEPT \
    -m conntrack --ctstate NEW \
    -j ALTA_LOG_ALLOW 2>/dev/null || \
iptables -I zone_lan_dest_ACCEPT 1 \
    -m conntrack --ctstate NEW \
    -j ALTA_LOG_ALLOW


# ============================================
# 4. Log LAN/VLAN Drop Decisions
# ============================================

iptables -C zone_lan_dest_DROP \
    -j ALTA_LOG_DROP 2>/dev/null || \
iptables -I zone_lan_dest_DROP 1 \
    -j ALTA_LOG_DROP


# ============================================
# 5. Log WAN Drop Decisions
# ============================================

iptables -C zone_wan_dest_DROP \
    -j ALTA_LOG_DROP 2>/dev/null || \
iptables -I zone_wan_dest_DROP 1 \
    -j ALTA_LOG_DROP

iptables -C zone_wan_src_DROP \
    -j ALTA_LOG_DROP 2>/dev/null || \
iptables -I zone_wan_src_DROP 1 \
    -j ALTA_LOG_DROP


# ============================================
# 6. Log VPN and WAN Allow Decisions
# ============================================

for CHAIN in \
    zone_wan_dest_ACCEPT \
    zone_vpn_dest_ACCEPT \
    zone_vpnMasq_dest_ACCEPT
do
    iptables -C "$CHAIN" \
        -m conntrack --ctstate NEW \
        -j ALTA_LOG_ALLOW 2>/dev/null || \
    iptables -I "$CHAIN" 1 \
        -m conntrack --ctstate NEW \
        -j ALTA_LOG_ALLOW
done

echo "Alta custom configuration applied."