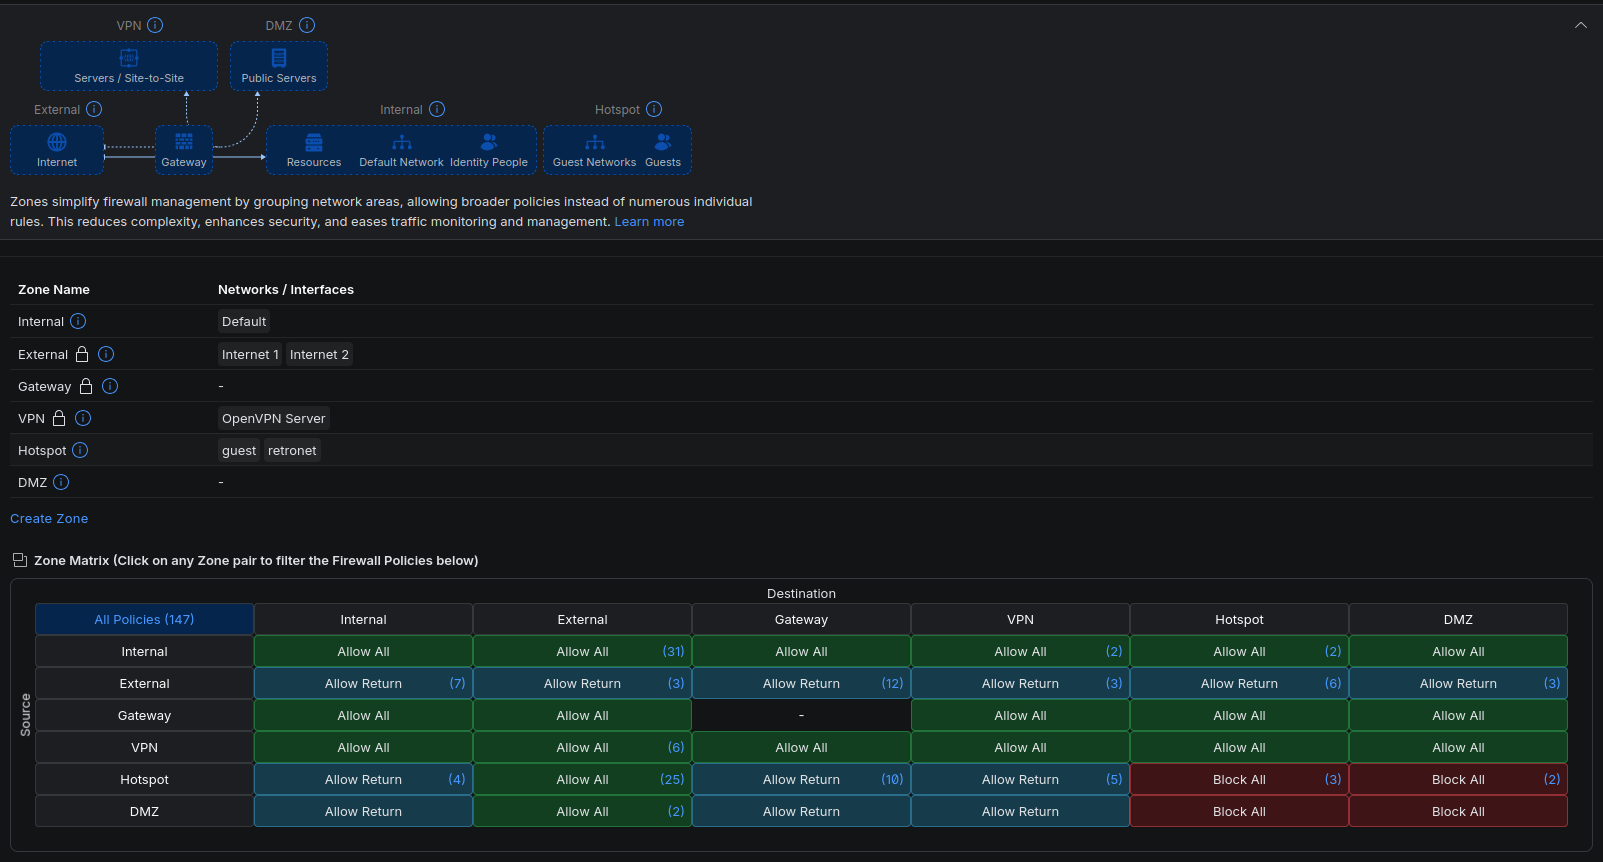
I do like the way that ubiquiti implmements zone based firewall and wonder if there’s a way to emulate this in the SSH/CLI? I attached how mine looks in my cloud gateway ultra
Is there a reason you want to move from the Unifi gateway? I use one with my alta switches and alta aps and it works great.
potential client’s needs.
Just to clarify, You are looking for the GUI to give you a grid rather than just make the rules?
Having asked about it before myself, perhaps the OP is wanting to create their own zones and define what is in it?
I would welcome that ability for multiple zones.
both
I can see wanting the gird as its a quick way to see what is or isn’t allowed. At the moment you could get mostly there by creating a Firewall group, call it whatever zone name you want, then add the subnets that belong to that zone. Then just make the rules you want by calling out the Firewall groups as the source or destination. Might be good to use a naming convention for Zone groups like ZN-DMZ or ZN-Guest-Wifi etc. I get that its not as quick and involves spending some brain CPU to investigate the rule. The benefit is that it scales better for larger more complex networks vs the simple Zone logic table.
I don’t have a route10 however I know it runs a modified version of openwrt.
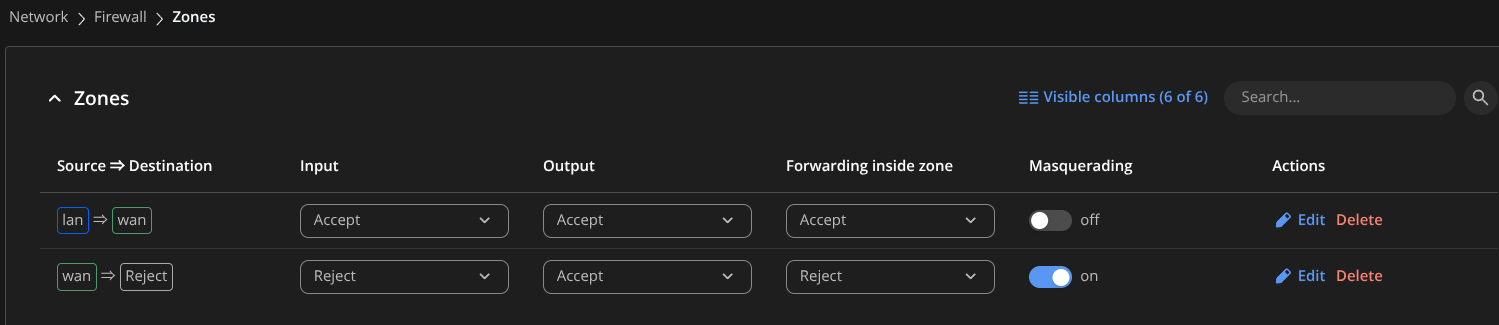
The vanilla openwrt or a modified version like RutOS (teltonika’s version of openwrt ) does have a firewall section that covers global zone settings (inter/ intra etc)
looks something like that
I guess this firewall section is missing /hidden in alta lab’s os?
well their facebook rep said they have it but it’s not exposed to the user. I’d like to bring this request more forward so more people can suggest that.
There’s at least 1 feature request in place for it we can vote on
I agrree, it is needed, however, I hope they can redesign it , as the venilla version of this page is rather confusing. They mixed things together, and if a user sees this page for the first time they might assume, they are accepting all the traffic from Wan etc, which is not the case but kind of looks like it..
yes. it does look confusing and needs broken down more, from what I have seen from others.