Ive rolled multiple rasp-pi’s and hosted vm’s with tailscale agent, configured as exit + proxy. While ive enrolled my Route10 as a node, approved & allowed a vlan, Tailscale shows connected (Route10 & Tailscale Dashboard) but unable to route traffic. Other nodes can ping Tailscale CGNAT address but nothing beyond ingress & egress.
A couple things from when I set this up recently:
- Is “Advertise Subnets” configured in your route10->Tailscale config?
- Linux clients have to be explicitly configured to accept routes, which can be done with
sudo tailscale set --accept-routes=trueafter they have been installed
Yes to both. I guess, with multiple VLANs, is it assumed all VLANS have access across the tailscale tunnel. Confusing to me if there is auto-configs taking place/routing behind scenes? or FW Rules I need to create
I use headscale, not the native tailscale control server, so this could be a bit different, but in Headscale, I believe I had to allow the route10 to advertise the routes after it connected.
If that doesn’t work, could you show a screenshot of your route10 Tailscale settings (blurring out anything sensitive)?
I tried to get this scenario to work and use it to access a remote tailscale enabled/router subnet.
Im at home with 192.168.42.0/24
would like to access 192.168.33.0/24
I added a static route to point the .33 subnet to be accessible via .42.1 (i.e my network) and no go. Without the static route no go either.
Not sure how I’ll get it to work but that’s how I had it setup when my raspi was by subnet router and had a static route on my router pointing at the raspi for that subnet.
Yes I appreciate a raspi is not a fw router.
We had this in the office on Friday, I completed setup but the routing table to return traffic wasn’t setup correctly during it being enabled.
I think it is Table 52 - check that when SSH’d in and you’ll see it as empty.
I was midway through adding a script to route return traffic correctly, when I happened to restart the tailscale service and it populated the table correctly.
So I would say check the table, see if it’s empty - if so restart tailscale via CLI and then see if it populates 
…there are some other quirks with the implementation right now that are unexplained, with dropped connections in some cases when trying to SFTP and I’ve just had the whole router go down when transferring a file to a NAS remotely. Bit of a shame coming from a Flint2 where the Tailscale implementation was rock solid.
Similarly have used Pis before as subnet routers and have had them work straight out of the box.
Thanks for the reports guys, I believe I’ve identified some of these issues and am working on them. Keep in mind this is a new feature. Thanks for the continued testing as we work through the bumps!
@S_NZ Can you provide additional detail on your setup? A network diagram would be helpful to understand the pieces. In my own setup, when using the advertise subnets config on route 10 I can reach those subnets without additional static routes.
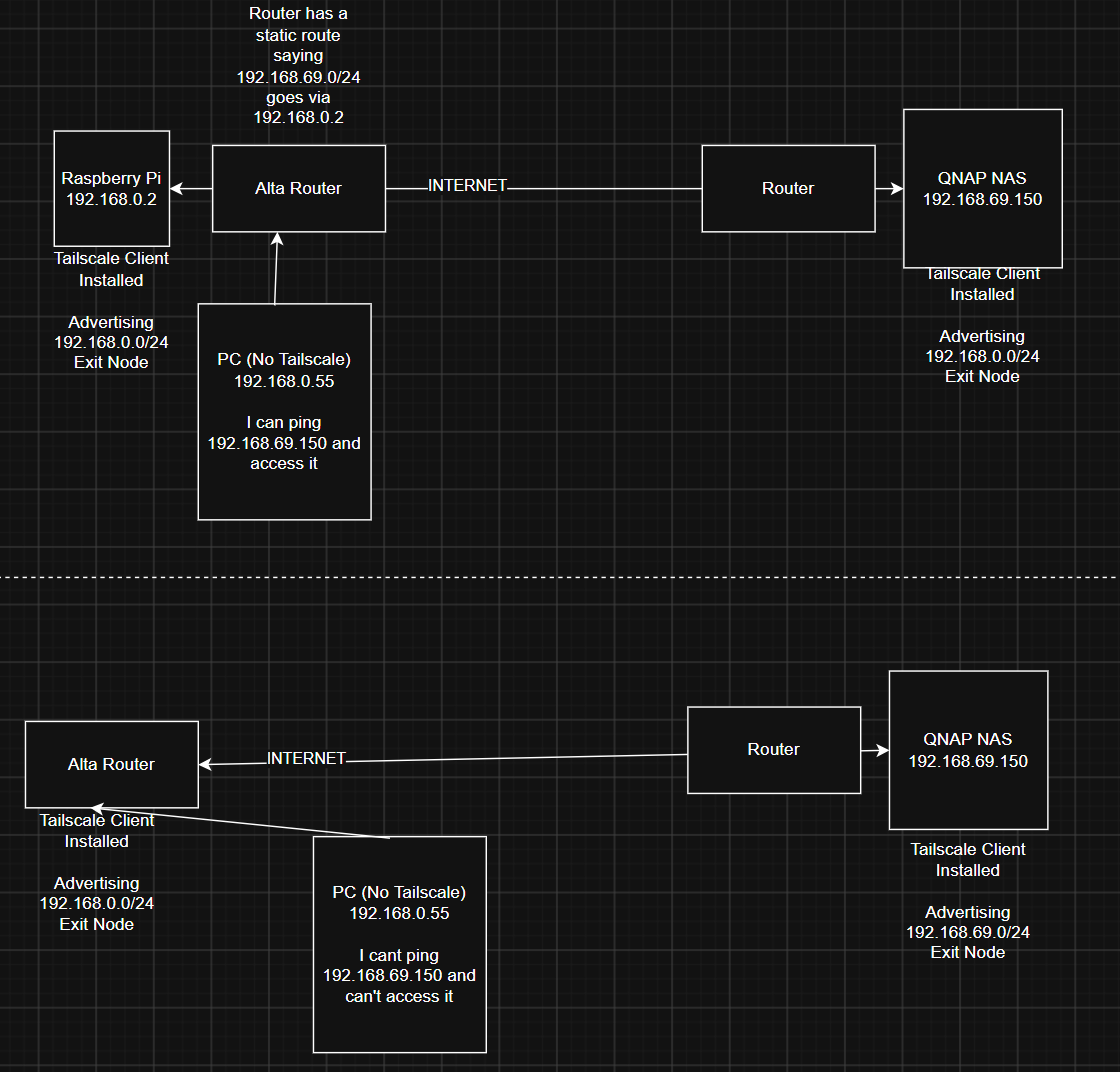
Here you go. First up is how I’m doing it now and second is what I tried to evolve it to!
If performance isn’t great I guess a 3rd Nirvana (for performance) would be if I can just have a Alta Router at both sites and sling a better performing VPN between them (probably fully route both subnets, but I should limit for security)
My setup is similar however, using multiple (5) VLAN’s on the Router10. Advertising (2) VLAN’s which were approved, etc.